January 7, 2027 | Virtual10:00 AM PST /10:00 AM CET /2:30 PM IST
Security for the autonomous era
Speakers
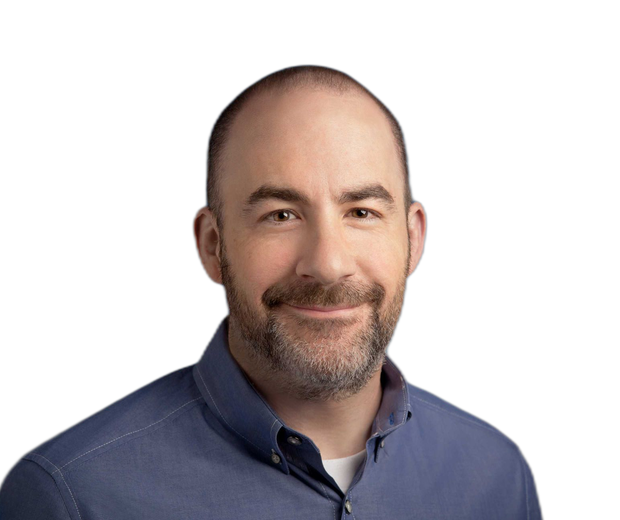
David Cross
CISO
Atlassian

John Morello
CTO & Co-Founder
Minimus

Kevin Catalon
Senior Expert, Risk & Resilience Practice
McKinsey
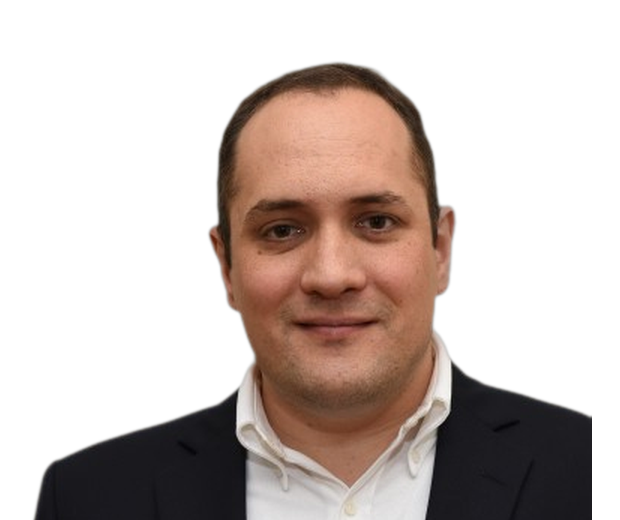
Emil Man
BISO
BCG

Jitender Aswani
SVP, Engineering & Security
Starburst

Ilya Kabanov
The Weather Report
Come with questions.
Cut through the hype
See where frontier models beat traditional testing, where they don’t, and how to run both.
Turn “found” into “fixed”
Automate triage, prioritization, and remediation so your response moves as fast as discovery.
Get ahead of autonomous attackers
Learn what changes when offense probes and adapts on its own, and how AppSec and API teams respond.
Put guardrails on your agents
Govern identity, permissions, tools, and data from first commit to production.
Agenda
10:00
10:25
The evolving frontier of LLMs in cyber defense
Frontier LLMs are opening up new possibilities in vulnerability discovery, especially for deep, reasoning-intensive analysis that can uncover subtle flaws and attack paths across complex codebases. But they are not a replacement for every existing security testing approach. This keynote explores where frontier models are changing vulnerability discovery, where traditional approaches continue to excel, and how security teams should think about fitting LLM-based scanning into their existing security stack.
Read more
Show less
Frontier LLMs are opening up new possibilities in vulnerability discovery, especially for deep, reasoning-intensive analysis that can uncover subtle flaws and attack paths across complex codebases. But they are not a replacement for every existing security testing approach. This keynote explores where frontier models are changing vulnerability discovery, where traditional approaches continue to excel, and how security teams should think about fitting LLM-based scanning into their existing security stack.

David Cross
Atlassian

Adam Arellano
Harness
10:30
10:55
Rethinking open source security in an AI world
Open source has always come with risk, but AI is changing how quickly vulnerabilities come to light—and raising expectations for how quickly organizations respond. As LLM-powered discovery puts more pressure on security teams, open source security has to evolve on two fronts: reducing the amount of vulnerable software organizations consume in the first place, and accelerating how quickly they can understand exposure, contain risk, and remediate when new vulnerabilities and zero-days emerge. This session explores both sides of that shift, from hardened software foundations to faster, more continuous response.
Read more
Show less
Open source has always come with risk, but AI is changing how quickly vulnerabilities come to light—and raising expectations for how quickly organizations respond. As LLM-powered discovery puts more pressure on security teams, open source security has to evolve on two fronts: reducing the amount of vulnerable software organizations consume in the first place, and accelerating how quickly they can understand exposure, contain risk, and remediate when new vulnerabilities and zero-days emerge. This session explores both sides of that shift, from hardened software foundations to faster, more continuous response.

John Morello
Minimus

Sanjay Nagaraj
Harness
11:00
11:25
From found to fixed at machine speed
As AI accelerates both software development and vulnerability discovery, it puts even more pressure on an existing security bottleneck: triaging, prioritizing, remediating, and deploying fixes fast enough to keep up. Finding more vulnerabilities doesn’t make organizations more secure if response can’t scale with discovery. This session explores how security teams can streamline the path from finding to fixing, automate the work between detection and remediation, and build a response process capable of operating at machine speed.
Read more
Show less
As AI accelerates both software development and vulnerability discovery, it puts even more pressure on an existing security bottleneck: triaging, prioritizing, remediating, and deploying fixes fast enough to keep up. Finding more vulnerabilities doesn’t make organizations more secure if response can’t scale with discovery. This session explores how security teams can streamline the path from finding to fixing, automate the work between detection and remediation, and build a response process capable of operating at machine speed.

Kevin Catalon
McKinsey

Emil Man
BCG

Rahul Sood
Harness
11:30
11:55
What changes when attackers become autonomous
AI isn’t only changing how defenders find vulnerabilities. It is giving attackers tools that can reason, adapt, explore applications and APIs, and iterate on attacks with far less human intervention. This session examines what changes when offensive activity becomes increasingly agentic, from faster reconnaissance and vulnerability exploitation to adaptive attacks that respond to defenses in real time, and what application and API security teams need to do differently to defend against them.
Read more
Show less
AI isn’t only changing how defenders find vulnerabilities. It is giving attackers tools that can reason, adapt, explore applications and APIs, and iterate on attacks with far less human intervention. This session examines what changes when offensive activity becomes increasingly agentic, from faster reconnaissance and vulnerability exploitation to adaptive attacks that respond to defenses in real time, and what application and API security teams need to do differently to defend against them.
12:00
12:25
Securing agents from development to runtime
Agent security is often framed as a runtime problem, but it doesn’t fit neatly into either traditional AppSec or runtime security. In production, agents can make dynamic decisions, invoke tools, access sensitive data, and take actions that create new runtime risks, but many of those risks can be reduced earlier by testing, governing, and constraining agents during development. This session explores why securing agents requires controls across the full lifecycle, from discovery and adversarial testing to governance and runtime protection, and how those controls need to work together.
Read more
Show less
Agent security is often framed as a runtime problem, but it doesn’t fit neatly into either traditional AppSec or runtime security. In production, agents can make dynamic decisions, invoke tools, access sensitive data, and take actions that create new runtime risks, but many of those risks can be reduced earlier by testing, governing, and constraining agents during development. This session explores why securing agents requires controls across the full lifecycle, from discovery and adversarial testing to governance and runtime protection, and how those controls need to work together.

Jitender Aswani
Starburst

Ilya Kabanov
The Weather Report
Emil Man
BCG
12:30
12:55
The agentic era: rethinking security when AI can act
Generative AI changed how software is created. Agents go further: they can make decisions, invoke tools, access data, call APIs, and take action on our behalf. That shift expands the security problem from protecting what AI produces to governing what AI is allowed to do. This closing keynote looks at how autonomy changes the attack surface, the controls organizations need around identity, permissions, tools, data, and behavior, and what security must become as AI moves from answering questions to taking action.
Read more
Show less
Generative AI changed how software is created. Agents go further: they can make decisions, invoke tools, access data, call APIs, and take action on our behalf. That shift expands the security problem from protecting what AI produces to governing what AI is allowed to do. This closing keynote looks at how autonomy changes the attack surface, the controls organizations need around identity, permissions, tools, data, and behavior, and what security must become as AI moves from answering questions to taking action.