
What Is a Type 2 (Type II) Error? Type I vs Type II
A type II error is one of two statistical errors that can result from a hypothesis test.
Security Testing Agent
What Is a Type 2 (Type II) Error? Type I vs Type II
Step into DevOps: where development and operations unite for agile software delivery. Embrace collaboration, automation, and constant improvement to transform how teams manage applications in the fast-paced digital world.
A type II error is one of two statistical errors that can result from a hypothesis test.
In software development, a software artifact refers to any output or result produced during the software development process, such as code files, documentation, executables, or configuration files. This article focuses on the importance of managing and maintaining artifacts throughout the software development lifecycle.
This article delves into Service Level Indicators (SLIs) as metrics used to measure the performance and reliability of a service. It explores how SLIs are defined, monitored, and used to establish Service Level Objectives (SLOs) to ensure that services meet predefined quality standards.
A merge conflict occurs in version control when changes made in different branches of code cannot be automatically merged due to conflicting modifications. Manual intervention is required to reconcile the differences and successfully integrate the changes into the codebase.
This article discusses canary deployments as a strategy for rolling out new software updates gradually to a subset of users before full deployment. It explores the benefits of canary deployments in reducing risks, gathering feedback, and ensuring a smooth transition to production.
Terraform is a cloud-agnostic Infrastructure as Code (IaC) tool that lets teams define, provision, and manage infrastructure using declarative code instead of manual setup. In this blog, you’ll learn what Terraform is, how it works, and when to use it. You’ll also explore its key components, use cases, and how it compares to other tools plus why OpenTofu has emerged as its open-source successor.
A staging environment acts as a final testing ground for software before it reaches production. This article explores how staging fits into the DevOps lifecycle, the architectural considerations involved in building one, and the best practices that ensure it serves its purpose: delivering secure, reliable, and performant releases.
You will learn what Agile delivery methodology entails, including how it fosters incremental development, feedback loops, and cross-functional collaboration. By understanding its principles, frameworks, and best practices, you’ll be equipped to implement Agile for faster value delivery and improved team morale.
SOX compliance doesn't have to be a bottleneck. By embedding automated controls, policy enforcement, and audit trails directly into the CI/CD pipeline, teams can meet strict regulatory requirements without sacrificing speed. This transforms compliance from a manual, after-the-fact hurdle into an integrated, seamless part of the development lifecycle, ensuring both velocity and governance.
Code repository tools play a pivotal role in modern software development by providing a structured way to store, track, and manage code changes over time. They form the backbone of DevOps workflows, facilitating collaboration, version control, and streamlined delivery. This article explores the essentials of code repository tools, highlights best practices, and discusses how AI-driven platforms like Harness are revolutionizing software delivery.
The takeaway here is that teams get into trouble when they automate a risky process just to run it faster. Teams that pair schema as code, backward-compatible application changes, visibility into what is deployed where, and policy-governed pipelines tend to ship faster and break less.
CI automates code integration, builds, testing, and security checks to catch issues early. Continuous Delivery keeps software production-ready while requiring a manual approval before release. Continuous Deployment removes the manual gate and automatically deploys successful changes to production. Continuous Deployment requires mature testing, observability, progressive delivery, feature flags, and automated rollbacks. For most teams, Continuous Delivery is the pragmatic target, balancing release automation with business and compliance requirements. Teams should move toward Continuous Deployment only when their automated guardrails are trusted and reliable.
A pull request is when you are requesting for someone in your org, possibly a senior engineer, to look at your code, review it, and pull the changes in.
A modern technology stack integrates various technologies and practices to address the complete lifecycle of an application, from development to deployment and maintenance. By carefully selecting and managing these technologies, organizations can build applications that meet current needs.

Release management is the strategic process of planning, coordinating, and controlling the deployment of software releases, ensuring they are delivered efficiently, reliably, and with minimal disruption to users or systems.
CI is frequent integration + automated verification, so teams merge small changes into a shared repository and validate every change automatically to catch issues early. Fast, trustworthy feedback is the goal, which means optimizing pipelines for speed and signal quality with small PRs, reliable tests, safe caching, and clear failure reports. CI is the foundation for modern delivery, because consistent builds, tests, artifacts, and traceability make it easier to scale governance, strengthen security, and move toward continuous delivery.
Unit vs Integration Testing: Differences & Best Practices
The Software Development Lifecycle (SDLC) is a structured approach to software development that outlines the steps involved in building and maintaining software systems. This article provides an overview of the different phases of the SDLC, and highlights the importance of following a systematic process to ensure the successful delivery of high-quality software products.
A container registry is built to store and distribute container images and speaks the Docker registry protocol, the same one Docker Hub and most cloud-native registries use. An artifact registry does that too, but it also manages the other outputs your build produces: Maven and npm packages, Helm charts, Python wheels, generic files, and more, all under one set of security and governance controls.
This guide reveals how to structure Terragrunt for multi-environment infrastructure at scale without sacrificing control. Learn proven patterns for DRY configuration, environment separation, and module management that keep your IaC maintainable as teams and deployments grow.
Continuous integration/continuous delivery (CI/CD) is a software development practice that focuses on automating the process of integrating code changes, testing them, and delivering them to production environments in a rapid and reliable manner. The article explores how CI/CD pipelines automate key stages of the software development lifecycle.
Mock testing is created to replicate the behavior of real components, enabling controlled testing of individual units and their interactions.
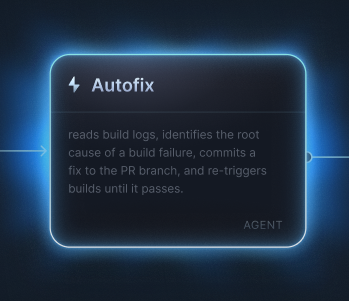
A worker agent is an AI agent that executes a delegated software delivery task as a step inside a delivery pipeline, rather than answering questions in a chat window. Worker agents operate in a loop: they receive a goal, plan an approach, call tools against real systems, verify their own output, and hand off a reviewable result such as a commit or a pull request. Because a worker agent runs inside existing pipeline infrastructure, it inherits that pipeline's access controls, policy enforcement, and audit trail instead of requiring a separate governance model.
One of the quickest ways to protect SLOs, stop Sev-1 incidents, and cut down on developer work without hiring more people is to lower the Mean Time to Detect (MTTD). You can lower MTTD by making alerts with a lot of signals, moving detection left into CI/CD and feature flags, and using AI to make every change "change-aware." Using templates, Policy as Code and scorecards to manage things makes sure that detection quality stays the same as you grow across teams, services, and clouds.
Learn what Static Application Security Testing (SAST) is, how it works, and why it’s essential for secure software development.
Standardizing OpenTofu CI/CD integration with reusable templates and GitOps workflows eliminates deployment bottlenecks and accelerates infrastructure automation at scale. Centralized governance, policy-as-code, and AI-powered verification are essential for maintaining security, compliance, and operational efficiency across hundreds of services. Harness Continuous Delivery & GitOps provides an enterprise control plane that unifies visibility, governance, and automated rollbacks, enabling teams to scale OpenTofu deployments safely and efficiently.
This guide explores how modern Artifact Registries like Harness AR enhance developer productivity by streamlining artifact management, accelerating CI/CD pipelines, and strengthening software supply chain security. Learn practical strategies to optimize your development workflow with efficient binary repository management.
The simple definition of DevOps is that it’s a cultural and professional movement, supported by practices and tools, that breaks down the traditional silos between software development and IT operations teams. The goal is to build, test, and release software faster and more reliably.
Run two production-capable environments (blue live, green standby) so you can deploy and validate the new version without disrupting users. Treat release exposure as a controlled traffic-routing change (load balancer/ingress/service switch or DNS), which minimizes downtime and makes cutover predictable. Get a fast rollback path by switching traffic back to the previous environment—especially effective when paired with strong verification and data-safe migration practices.
Smoke tests are quick, automated checks that find release-breaking problems immediately after deployment and prevent unstable builds from progressing. Strong smoke testing stays small and dependable: a few important checks, clear assertions, and a predictable runtime so that teams can trust the gate. Automation and smoke tests go well together because they make sure that the pipeline is always gated, create rich failure artifacts, and (when needed) verify the deployment using real health signals (metrics/logs) to help make safe rollout decisions.
Infrastructure as code security is a workflow problem, not a scanning problem. Secure changes must flow through Git, pipelines, and policy. Start with non-blocking IaC security checks. As noise decreases and trust increases, tighten controls gradually. Real security means the only way to change infrastructure is through secure, automated pipelines safe by default. Harness Infrastructure as Code Management brings Terraform/OpenTofu, policy as code, drift detection, and cost controls into one auditable workflow.

Mean Time Between Failures (MTBF) tells you how often your systems fail, but if you only look at it, you might end up shipping slower and taking on more risk instead of less.The real value comes from keeping an eye on MTBF along with the change failure rate, deployment frequency, and mean time to recovery. That's how you get things out faster and still be reliable.With automation, canary deployments, and automated verification, modern continuous delivery can help you improve MTBF while also speeding things up.
This article delves into the concept of policy as code, where policies and compliance rules are defined and enforced through code. It explores the benefits of implementing policy as code in ensuring consistency, security, and governance across cloud environments and infrastructure.
An internal developer platform is way more than just a catalog. It's a thoughtfully designed layer that gives developers safe, self-service access to infrastructure and delivery workflows. The secret sauce? Treat your platform like a product. That means clear ownership, real metrics, and feedback loops that actually work. Start small and win big. Focus on narrow, high-value workflows like one-click service onboarding and trusted catalogs instead of trying to boil the ocean.
A unified DevOps platform brings together CI/CD, testing, security, and governance into a single solution, eliminating tool sprawl and enabling faster, more reliable software delivery. Modern DevOps platforms come with built-in security and compliance controls that support SLSA L3 compliance, automated governance, and easy migration from older tools like Jenkins.
Infrastructure as Code tools only work when Git is the single source of truth and pipelines, not people, run, plan and apply. Most IaC failures come from process problems: unmanaged state, unclear environments, over-engineered modules, and manual drift. A mature IaC setup is safe, predictable, auditable, and easy to roll back usually by reverting a pull request. If you can’t answer “what’s in production, who changed it, and why?” from Git alone, your IaC isn’t finished.

What is NuGet? NuGet is the official package manager for .NET, a tool that makes it easy for developers to add, update, and share reusable code across projects. At its core, NuGet simplifies dependency management by providing a central hub for discovering and installing libraries, frameworks, and tools. When you hear “NuGet package,” think of it as a neatly wrapped bundle of compiled code, configuration files, and metadata. These packages can contain everything from a single helper library to a full-featured framework. Instead of manually downloading files and configuring paths, you can simply run a NuGet command, and the package is installed—along with any other packages it depends on. If you’ve used package managers like npm (JavaScript), pip (Python), or Maven (Java), NuGet plays the same role for the .NET ecosystem.
Maven standardizes how Java projects are built and how dependencies are managed, making development more consistent and repeatable. By automating dependency resolution and using a structured build lifecycle, it reduces manual work and errors. When paired with a private repository like Harness Artifact Registry, teams gain better control, security, and reliability across their software delivery process.
Helm simplifies Kubernetes deployments by packaging complex configurations into reusable, consistent charts. When combined with Harness, teams gain centralized management, security, and seamless CI/CD integration. This enables more reliable, scalable, and automated application delivery across environments.
In this article, you’ll learn why ephemeral environments are becoming a foundational practice in modern DevOps, how they improve developer velocity and software quality, and—critically—how to implement them without sacrificing security, governance, or compliance. We’ll explore common risks, best practices, and architectural patterns that help organizations balance speed with control.
Environment as a Service (EaaS) is an approach to provisioning and managing software environments through automated, self-service workflows. Instead of relying on manual tickets or ad-hoc scripts, teams consume environments on demand using standardized templates and guardrails. This article explains what EaaS is, its defining characteristics, and the key tradeoffs organizations should consider when adopting an EaaS model.
To scale CI/CD pipelines, templates should be referenced - not copied. Reuse by reference enables more efficient maintenance. This guide introduces the Pipeline Reuse Maturity Model.
Consider features, migration and AI capabilities when choosing your next CI/CD platform.
PCI DSS 4.0 rigorous compliance demands create tension with business imperatives to move quickly . The key to achieving continuous compliance without slowing down excessively is to embed automated security and governance directly into your CI/CD pipeline.

What is a false positive rate, and how is it calculated? How does it compare to other measures of test accuracy, like sensitivity and specificity?
In software, value is a function of delivery. You can have the most elegant code, the most innovative features, and the most brilliant engineering team, but until that product is running in production, its value is purely theoretical. Product deployment is the process that turns potential value into actual value. It’s the entire sequence of activities that takes completed code from a developer’s machine and makes it available to end-users.
Software Artifacts are the raw outputs of development, while software packages are curated, versioned artifacts ready for distribution and confusing the two can lead to security risks, inefficiency, and wasted costs. In this blog, we will help distinguish between them, so that teams can apply the right governance, accelerate pipelines, and maintain compliance. Harness Artifact Registry unifies both worlds with universal storage, end-to-end traceability, and built-in security to help teams ship faster, safer, and smarter.
Discover the essentials of software testing—functional and non-functional—to improve app performance, reduce bugs, and boost user satisfaction. Learn about unit, integration, end-to-end, and performance testing, plus best practices for manual and automated approaches.
To meet demands for faster, more frequent releases, organizations must master continuous delivery. This practice automates the deployment pipeline, making releases safe, fast, and repeatable.
Discover DevOps' meaning and explore its principles, benefits, and best practices for effective collaboration and automation.
Discover top DevOps tools characteristics for seamless CI/CD automation and enhanced team collaboration.
Progressive Delivery is a modern software release strategy that enables teams to deploy changes safely, incrementally, and with minimal risk. In this article, you will learn what Progressive Delivery is, why it is crucial for modern DevOps practices, and how it enhances software delivery through real-time feedback and data-driven decision-making. You will also dive deeper into the core principles, benefits, challenges, and best practices for implementing Progressive Delivery effectively.
Decoupling deployment from release empowers development teams to innovate faster and more safely. By deploying code changes behind feature flags or other mechanisms, organizations can gain fine-grained control over when, how, and to whom new features are exposed. This approach reduces risk, improves user experience, and provides a more flexible path to continuous delivery and experimentation.
Software engineering metrics help teams quantify performance, quality, and efficiency across the software development lifecycle. In this guide, you’ll learn what metrics matter most, why they’re crucial for engineering organizations, and how to implement them effectively to improve velocity, reliability, and alignment with business goals.
Feature flags in production empower organizations to release software changes with minimal risk. In this article, you will learn how to implement feature flags effectively, manage real-time rollouts, and adopt best practices for robust testing in production environments.
Continuous integration (CI) revolutionizes software development by automating code integration, testing, and builds. This article explores the key benefits of CI, including improved software quality, faster delivery times, and enhanced team collaboration, empowering Agile teams to stay competitive in a fast-paced industry.
This article will help you understand how Kubernetes networking works—from internal service discovery to exposing apps externally with Ingress. You’ll learn what Services are, how Ingress fits in, and how traffic flows through a Kubernetes cluster.
Infrastructure as Code (IaC) transforms how organizations provision and manage IT infrastructure by replacing manual processes with machine-readable definition files. This approach brings software development practices to infrastructure management, enabling teams to automate deployments, ensure consistency, and integrate infrastructure changes into DevOps workflows for more reliable and efficient software delivery.
Learning Infrastructure as Code (IaC) enables teams to provision, manage, and destroy compute resources through declarative code instead of manual processes. In this article, you’ll explore foundational concepts, best practices, and tools that help you adopt IaC seamlessly—empowering you to reduce errors, increase scalability, and accelerate software delivery.
An artifact registry for multi-cloud environments provides a centralized repository system that securely stores and manages software artifacts across multiple cloud platforms. This guide will help you understand how to implement and optimize artifact registries to improve developer productivity, strengthen security, and streamline your CI/CD pipeline in multi-cloud environments.
Cloud source code repositories have transformed software development by enabling seamless collaboration, scalability, and robust security. This article explores their benefits, features, and role in modern software delivery workflows.
In this article, you will learn how artifact registry automation tools streamline software development workflows by securely storing and versioning application components, such as binaries, container images, and libraries. We will explore essential features, best practices for security, and ways to integrate artifact registries seamlessly into your CI/CD pipeline.
You will learn proven strategies for managing reliability in cloud-native environments. This includes understanding core principles, essential tools, and organizational best practices that ensure resilience and continuous delivery in complex systems.
System chaos is inevitable in today’s complex, distributed software environments. Adopting chaos engineering strategies—especially those enhanced by AI—helps organizations proactively identify vulnerabilities, maintain consistent performance, and deliver reliable services to end-users. This article explores how to understand system chaos, implement chaos engineering tools, and leverage AI-powered platforms like Harness to thrive in the face of continual change.
When it comes to software architecture, there's no one-size-fits-all solution. The debate between monoliths and microservices continues to challenge engineering teams globally. This guide will help you understand the fundamental differences, evaluate which approach aligns with your organizational needs, and learn practical strategies for implementation or migration between these architectural styles.
This article explores how to effectively measure internal developer portal (IDP) usage, identify adoption barriers, and drive value across engineering organizations. You’ll learn about key metrics, data sources, and actionable insights to improve platform adoption and enhance developer experience.
Optimizing Git performance at scale is essential for maintaining developer productivity and ensuring fast, reliable workflows in large organizations. This article explores the technical challenges of scaling Git, practical optimization strategies, and how modern teams can leverage configuration, infrastructure, and monitoring to keep repositories fast and efficient as they grow.
Learn how to implement IaC in CI/CD pipelines for faster, more reliable deployments. Explore best practices, tools, and workflows in our guide.
Implementing infrastructure as code (IaC) revolutionizes how you manage, deploy, and scale your technology environments. In this guide, you will learn the core principles, best practices, and critical steps for successful IaC adoption—from version control to automating your entire environment lifecycle.
If you're wondering how to access a Kubernetes pod from outside the cluster, this article will walk you through the most effective methods, like services, port forwarding, and ingress controllers. You’ll learn how Kubernetes networking works and the best approach for different use cases.
In this article, you’ll learn how to build a developer portal that developers actually want to use. We cover the essential components, benefits, challenges, and best practices, helping you align your developer portal to real business and engineering goals.
This article delves into how internal developer portals (IDPs) foster team collaboration by centralizing tools, streamlining communication, and enabling seamless workflows. You’ll learn the role of IDPs in breaking down silos, key features that enhance teamwork, and strategies to maximize their impact, ensuring teams deliver software faster and more efficiently.
Capacity planning in Site Reliability Engineering (SRE) ensures systems are robust, scalable, and cost-efficient. By accurately forecasting resource needs, organizations can maintain high availability while avoiding overprovisioning. In this article, we’ll explore the fundamentals, best practices, and tools you can leverage to stay ahead of capacity demands and streamline your reliability strategy.
Data privacy is a cornerstone of feature experimentation, providing the trust and compliance needed to launch new and impactful features. In this article, you’ll learn the significance of protecting user data, common challenges, and how effective privacy strategies help maintain innovation while meeting regulatory demands.
Proactive incident prevention in Site Reliability Engineering (SRE) focuses on building resilient systems that avert critical failures long before they happen. Organizations can dramatically reduce incidents by leveraging observability, chaos engineering, well-defined SLOs, and advanced software delivery solutions like Harness, and dramatically reduce incidents and maintain user satisfaction in today’s fast-paced digital landscape.
This article explores how effective governance ensures that internal developer portals remain secure, compliant, and well-maintained. We will cover best practices for policies, permissions, and automation that keep the portal in line with organizational standards while enabling developers to work autonomously.
Feature release strategies serve as the backbone of modern software delivery. In this article, you will learn how various strategies—from canary releases to blue-green deployments—empower you to deploy changes more effectively, reduce risk, and deliver value faster. Whether you’re part of a small startup or a global enterprise, understanding these approaches ensures stable releases and satisfied users.
Continuous Integration (CI) in microservices architecture enables teams to independently build, test, and integrate small, modular services for faster, more reliable software delivery. This article explores the unique challenges and best practices of implementing CI in a microservices environment, empowering organizations to achieve agility, scalability, and quality at scale.
Scaling artifact registries is critical for managing the growing volume of software artifacts—think container images, binaries, and packages—in modern development environments. By reading this article, you’ll learn practical approaches to building resilient, high-performing artifact repositories that can handle large-scale demands and support continuous delivery. You will also gain insights into best practices such as automation, multi-cloud replication, and robust security measures.
In this article, you will explore the best DevOps automation tools that help teams accelerate software delivery, reduce human error, and improve system reliability. Learn how these tools fit into the DevOps lifecycle and why choosing the right stack is critical to achieving engineering excellence.
By reading this guide, you will learn how to set up automated processes for artifact creation, tracking, and governance throughout software delivery. You’ll discover how automation can reduce manual errors, speed up deployments, and ensure compliance in fast-paced development environments.
Learn what Jenkins CI is, how it facilitates continuous integration in software development, and the key features that make it a popular choice among DevOps teams. You'll also gain insights into the benefits of using Jenkins to streamline your software delivery pipeline.
Learn how to integrate compliance requirements seamlessly into your database DevOps lifecycle, prevent regulatory pitfalls with automated checks, and foster a culture of continuous compliance for a more secure and efficient delivery pipeline.
A good internal developer portal centralizes tools, documentation, and resources to streamline developer workflows and reduce friction. By emphasizing user-centric design, robust integrations, security, and self-service, teams can boost productivity, accelerate deployments, and create better developer experiences.
A Developer Platform (DP) is a centralized platform that unifies developer workflows, tools, and resources to streamline software delivery within an organization. A DP empowers teams to innovate faster, reduce complexity, and enhance overall collaboration by consolidating DevOps processes, best practices, and supporting technologies. This article explores how a DP works, why it is critical for modern software delivery, and how a robust solution like the Harness AI-Native Software Delivery Platform can drive operational excellence.
DevOps Database Management bridges the gap between traditional database administration and modern continuous delivery practices. In this guide, you’ll learn how integrating databases into DevOps workflows can reduce errors, accelerate delivery cycles, and foster better team collaboration.
Learn what Atlassian Compass is—a developer experience platform designed to manage distributed software architectures—and explore its core features like component catalogs and health scorecards. You’ll also understand its strengths, limitations, and how it stacks up against more comprehensive internal developer portals, helping you decide if it’s the right fit for your engineering team.
Gain a clear understanding of artifact storage security, the primary threats affecting software artifacts, and the best practices for protecting and managing these critical assets. You’ll also discover how to implement effective security measures and maintain compliance while ensuring a streamlined development workflow.
Code repository analytics provide developers and organizations with actionable insights into codebase health, team productivity, and collaboration efficiency. By leveraging advanced metrics and tools, you can optimize workflows, identify bottlenecks, and improve software quality.
Object dependency shapes how software components interact, influencing everything from feature rollout to maintenance. By understanding these intricate dependencies, you’ll learn strategies to prevent conflicts, ensure seamless feature access, and foster more efficient software delivery.
Long-term dependencies and slow feature analysis can significantly hinder development velocity and organizational agility. In this article, you will learn how these challenges emerge, why dynamic process monitoring on GitHub helps address them, and which strategies can minimize bottlenecks for better software outcomes.
Internal Developer Platforms and Internal Developer Portals are distinct yet complementary solutions designed to improve software delivery and empower developers. By reading this article, you’ll learn the defining features, benefits, and challenges of each, and gain insights into choosing the right approach to optimize your developer experience.
Continuous fuzzing with LibFuzzer and AddressSanitizer is a powerful technique for identifying software vulnerabilities. This guide explores how these tools work, their benefits, and best practices for integrating them into your development process.
Learn how to choose and manage a code repository tailored specifically for microservices architecture. We'll cover repository types, best practices, common pitfalls, and strategies to optimize your development workflow.
A chaos lab is more than just a testing environment—it’s a strategic investment in your system’s ability to withstand real-world failures. By integrating chaos experiments into your DevOps pipeline, you proactively uncover weaknesses and boost resilience and overall reliability—making your software delivery process robust and future-proof.
Database DevOps observability is the cornerstone of modern software delivery, enabling teams to detect issues early, implement real-time fixes, and ensure continuous reliability. By leveraging the right tools and best practices, organizations can unify databases, infrastructure, and application layers—creating a high-velocity pipeline without compromising quality or security.
Database DevOps tools play a critical role in bridging the gap between traditional database administration and modern development workflows. By streamlining database changes and automating repetitive processes, organizations can deploy software more quickly, reduce errors, and improve overall system reliability.
Database security in DevOps environments is critical for protecting sensitive information and maintaining high availability. In this article, you’ll discover the most effective database security practices and how to integrate them seamlessly into DevOps workflows. You’ll learn how to address common security vulnerabilities, implement encryption, establish robust access controls, and automate security checks at every stage of the software delivery pipeline.
Learn the core principles and best practices for managing artifact dependencies effectively within modern software delivery. You’ll explore the key challenges, strategies for version control, security considerations, and how automation can streamline your dependency management process.
Learn proven techniques and principles for designing, implementing, and maintaining a scalable developer portal. You’ll discover how to address common challenges, adopt high-performance architectures, and leverage automation to empower teams and drive growth.
Get Started
Try the full platform free. No module restrictions, no credit card.